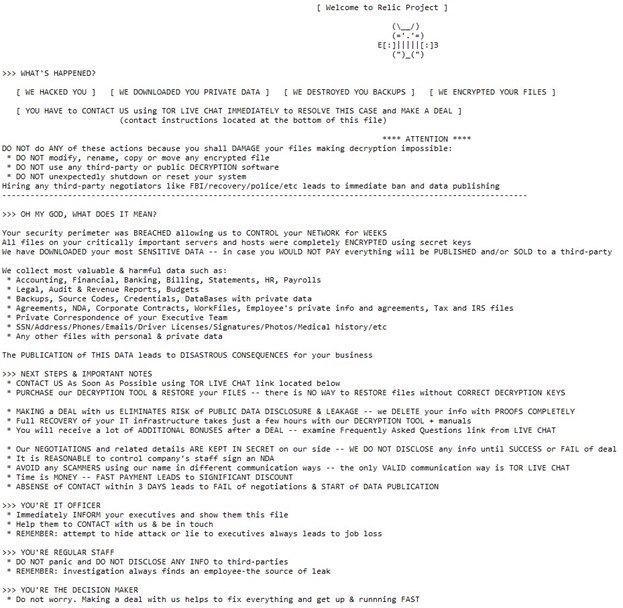
A ransom note, UNLOCK_FILES.793DF82AFCB81B75.txt, appeared on
computers throughout a company and when triaging what happened,
encrypted files were observed. The ransom note (shown below) gave
specific instructions as to what was happening, details on how to
resolve the problem and a link where to contact them.
A typical ransomware response was initiated, and forensic
analysis was completed. An unpatched FortiGate appliance, which
controlled Remote Desktop Protocol (RDP) access for users, was
found to be the likely entry point into the environment.
This vulnerability allows any user to connect without having to
authenticate, allowing access and granting administrator
privileges. This access was leveraged and a user account was
created that had a similar name to that of a legitimate
administrator account. PSEXESVC was executed which let users
execute processes on remote systems without the need to have any
kind of client software present on the remote computers.







